Microsoft OneLake
Microsoft OneLake is a unified data lake for the whole organization. It comes automatically with every Microsoft Fabric tenant.
Install Microsoft OneLake from the community library
Complete the following steps to install the Microsoft OneLake connector from the community library:
Open the recipe editor and search for a connector. Alternatively, you can search for a connector in the community library.
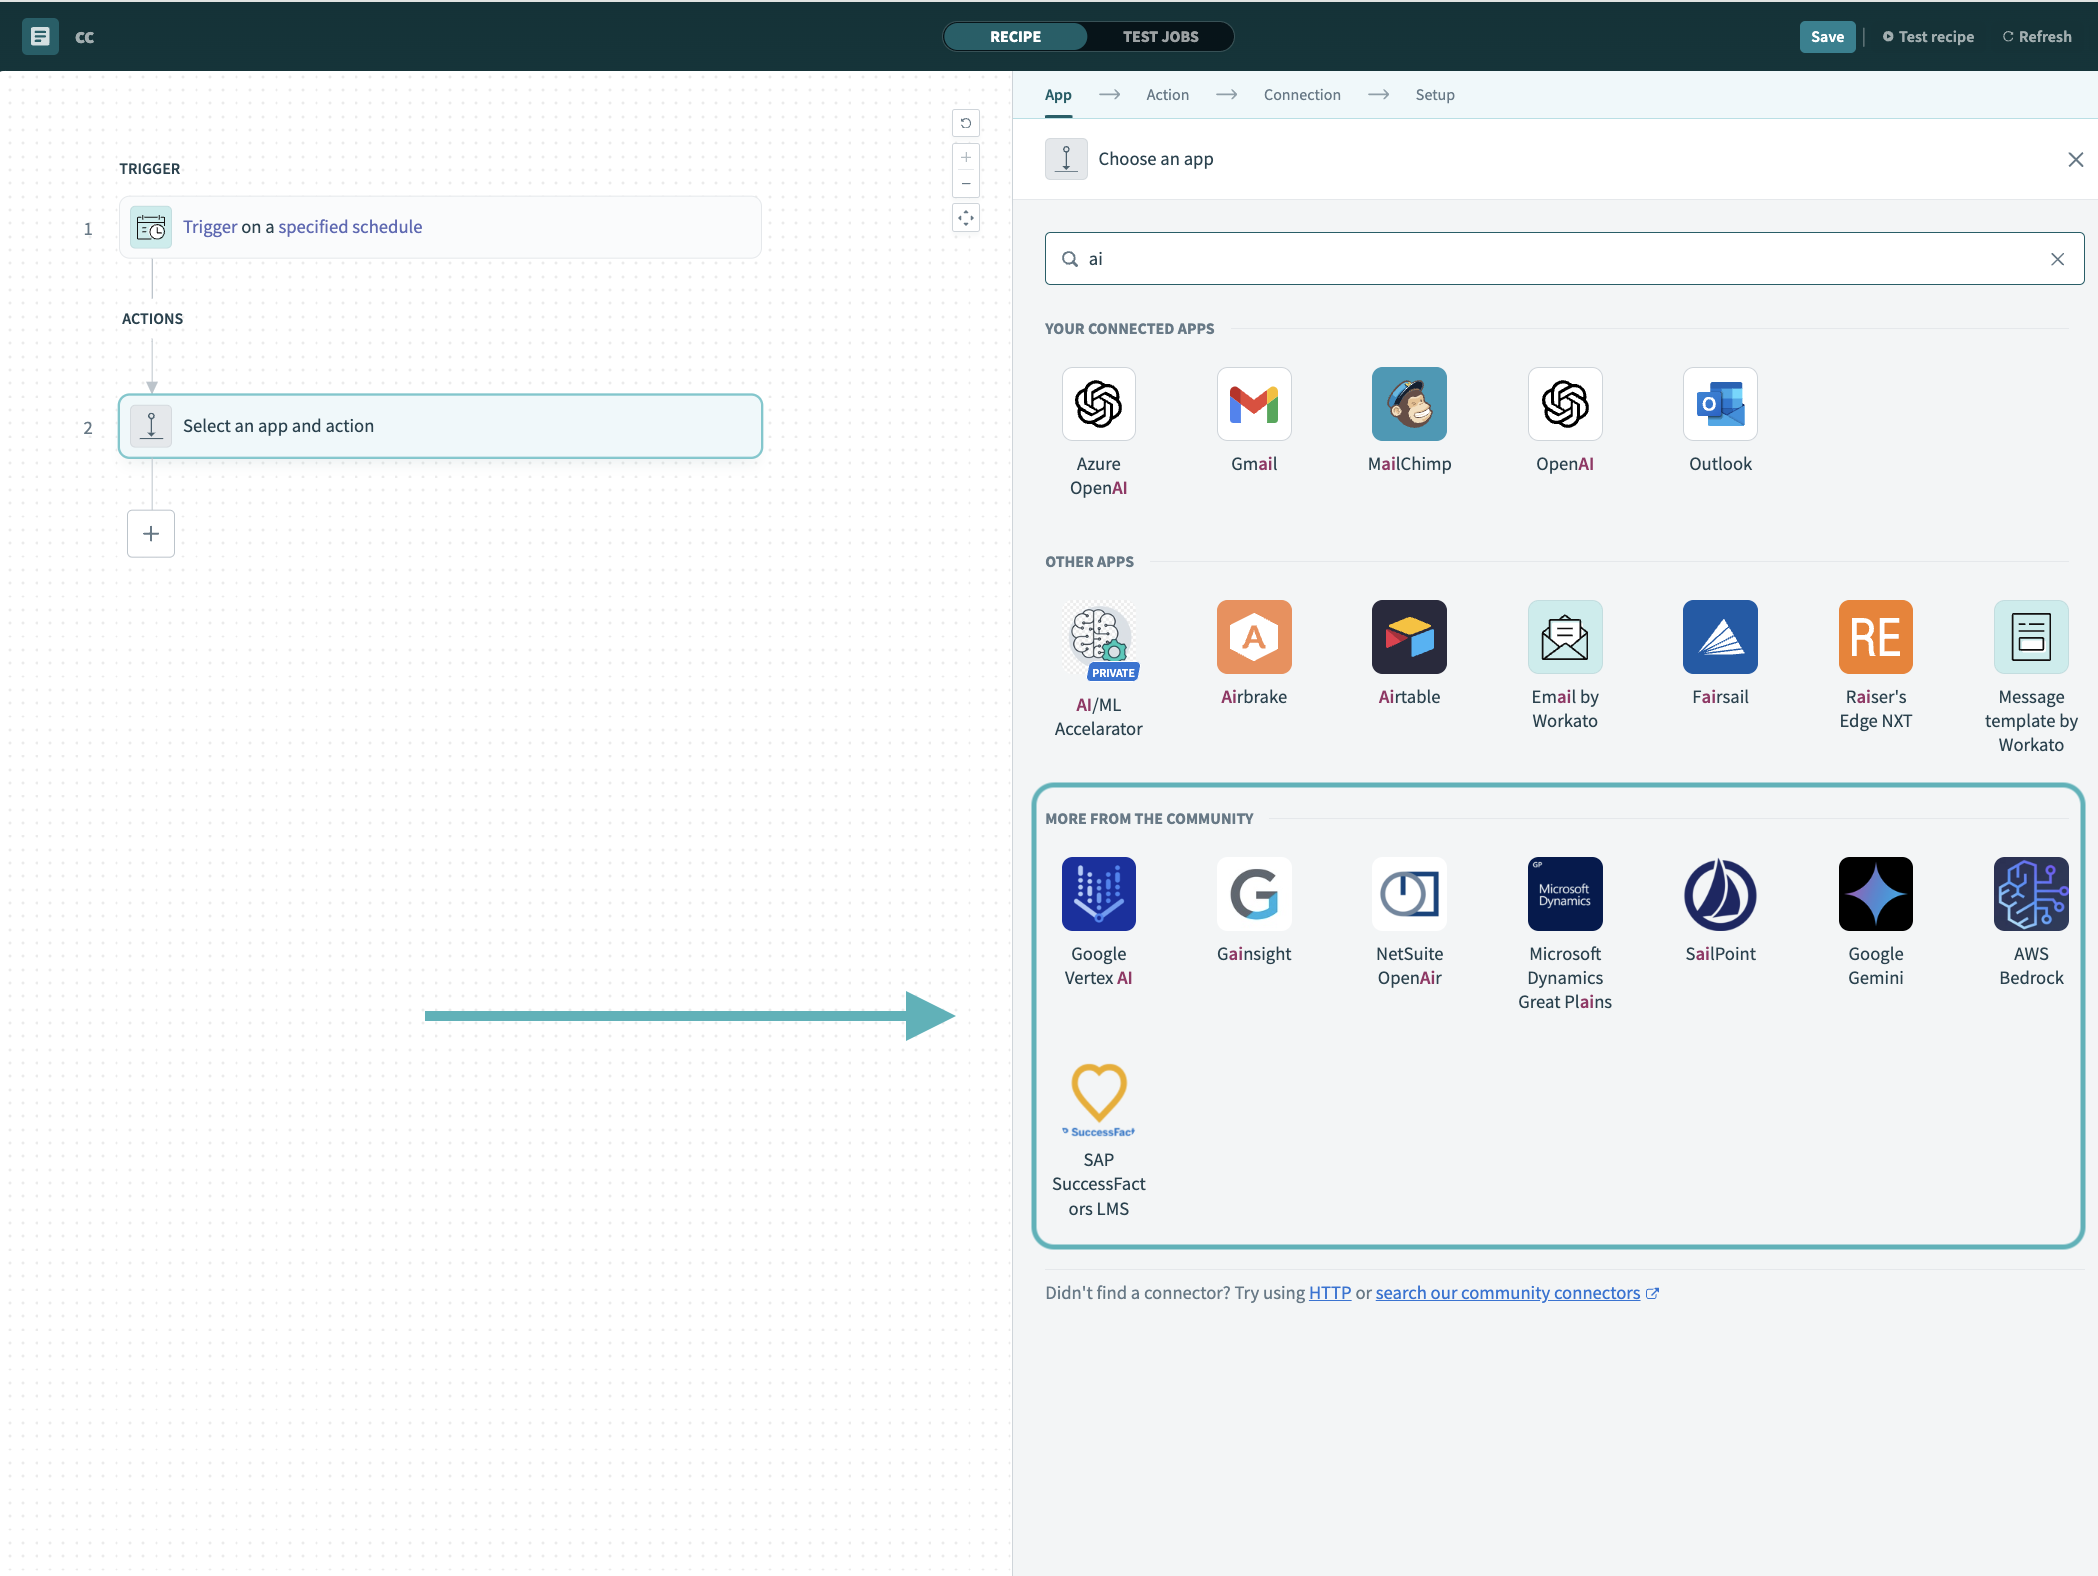 Search for community connectors in the recipe editor
Select the community connector you plan to install.
Click Install to install the connector from the community library.
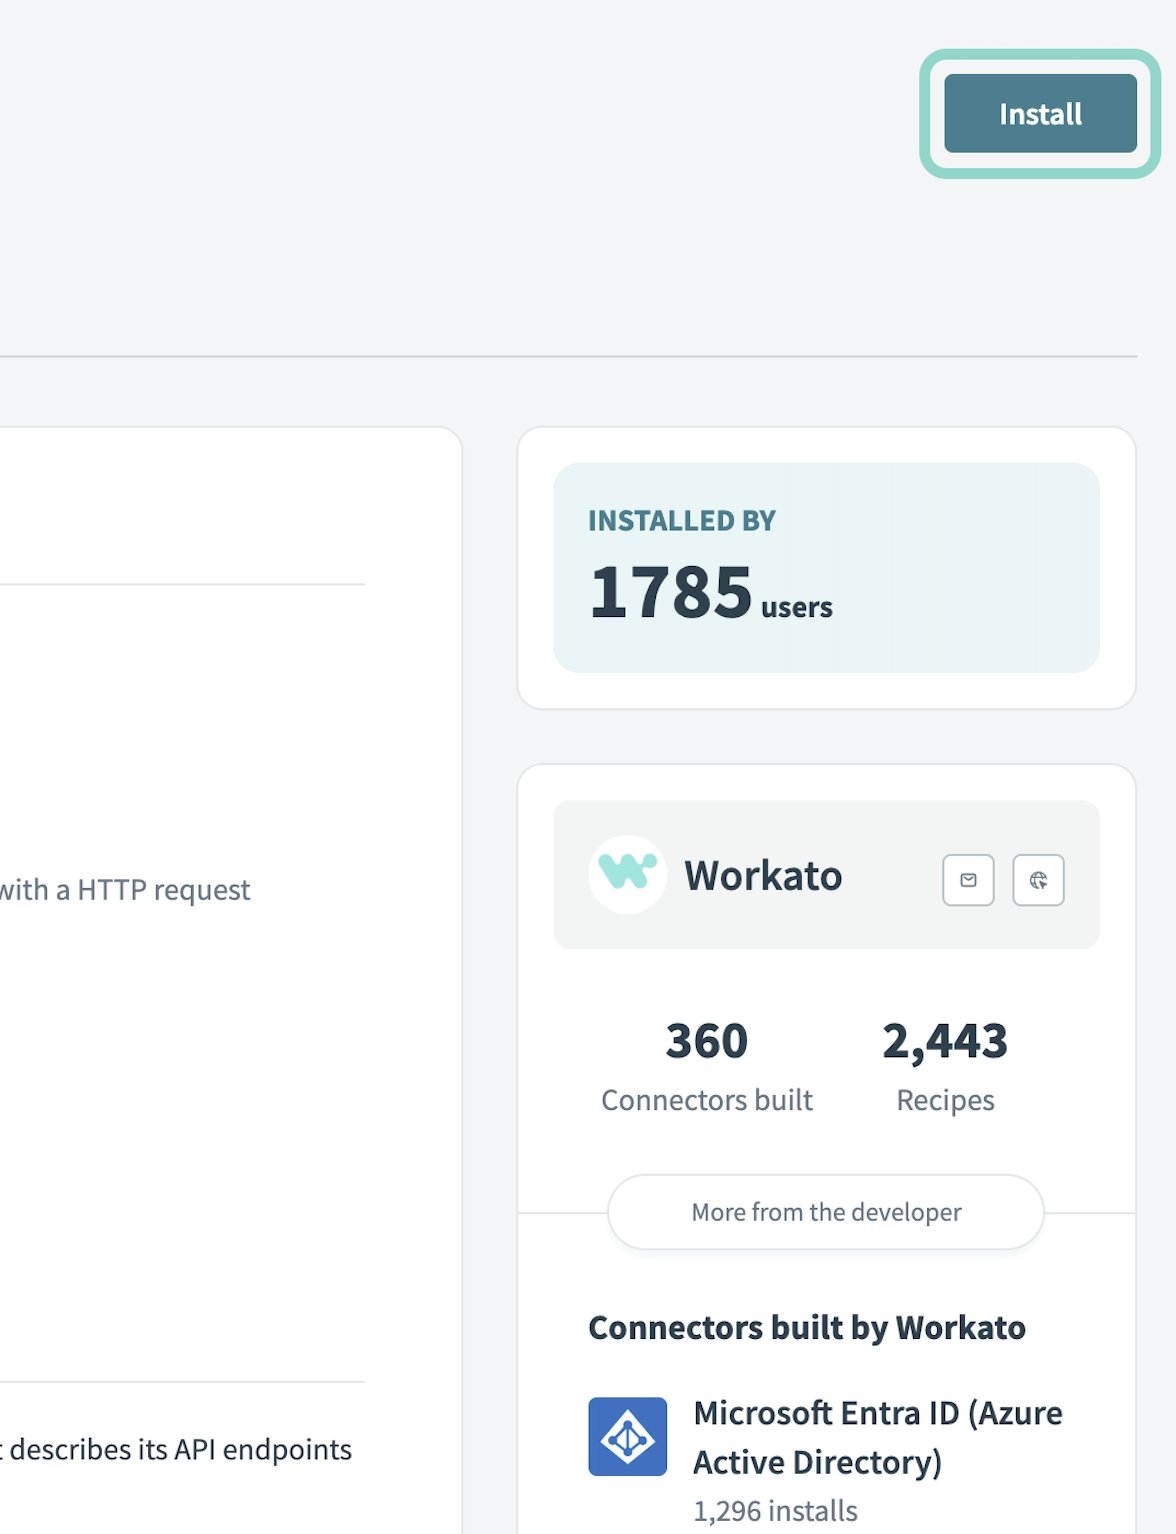 Click Install
Select Release connector. Alternatively, select Review code to review and modify the connector code before releasing it to the workspace.
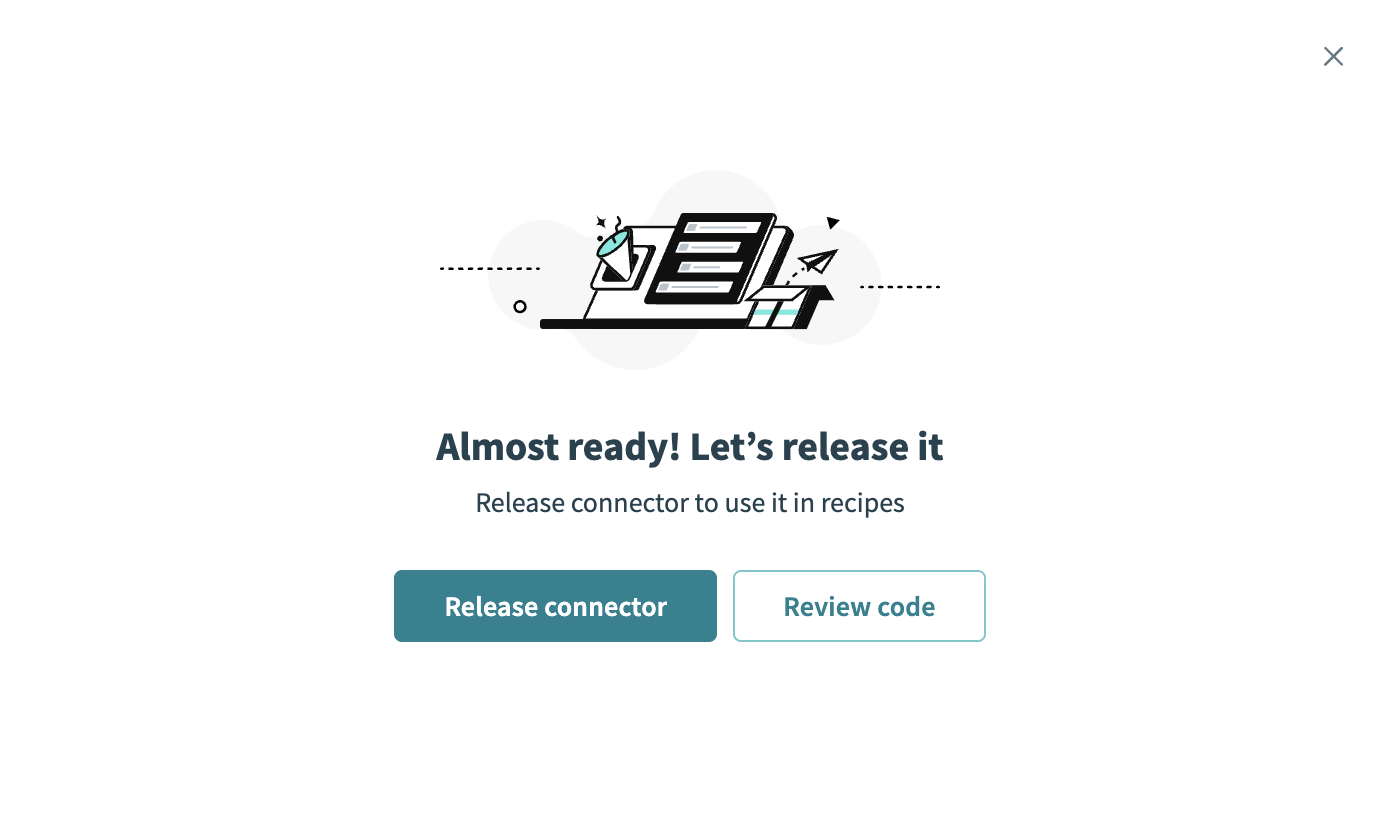 Release the connector
Summarize any changes you made to the connector, then click Release to allow workspace collaborators to use the connector in recipes.
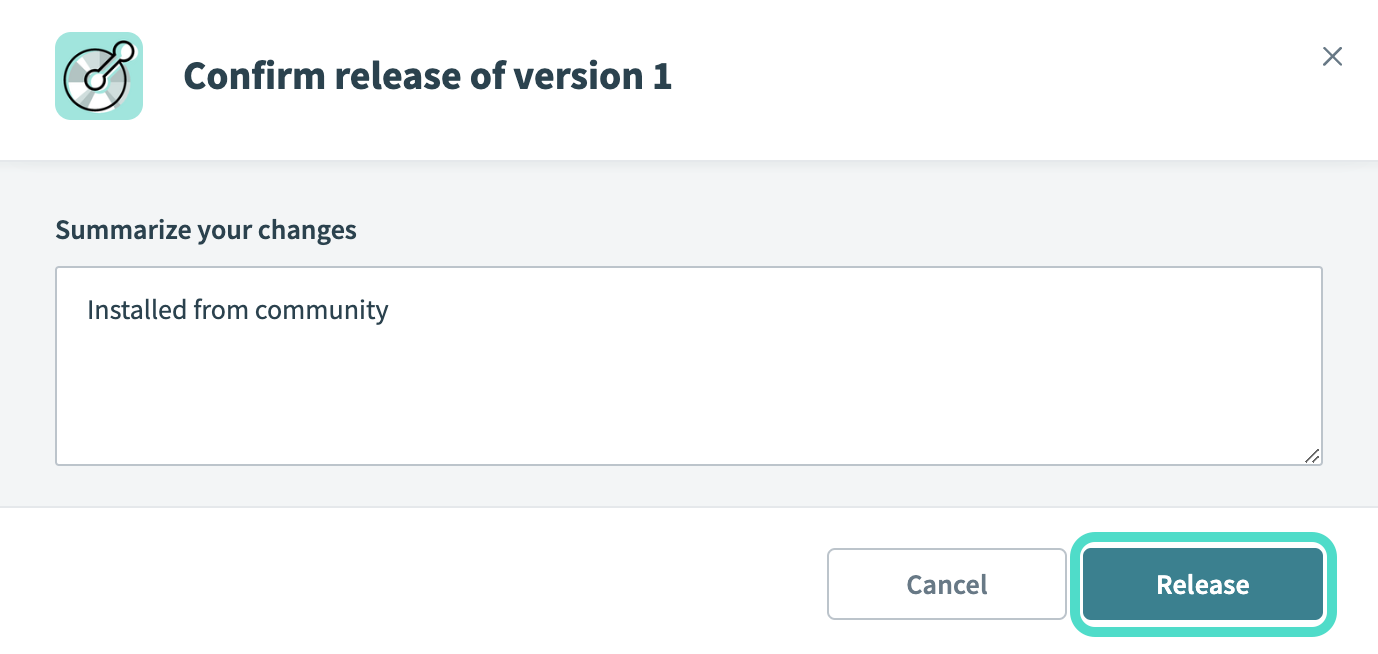 The Confirm release dialog
Connection setup
The Microsoft OneLake connector supports the following authentication types:
- Authorization code grant authentication (OAuth 2.0): Acts as the Microsoft user who authorizes the connection
- Client credentials-based authentication (OAuth 2.0): Acts as a service principal, without a signed-in user
MICROSOFT MFA ENFORCEMENT
Microsoft is rolling out mandatory multifactor authentication (MFA) gradually to different applications and accounts in phases. This enforcement continues throughout 2025 and beyond. Refer to the Microsoft Mandatory multifactor authentication for Azure and admin portals documentation for more information.
We strongly recommend enabling MFA now for all Microsoft accounts used with Workato to avoid service disruptions from short-notice enforcement changes.
Complete the following steps to maintain uninterrupted service:
Enable MFA for your Microsoft organization following the Microsoft MFA setup guide. Refer to Set up multifactor authentication for Microsoft 365 for more information.
Reconnect your Microsoft connection in Workato.
Complete the OAuth flow with MFA when prompted.
Test your recipes to ensure they work with the updated connection.
Authorization code grant authentication (OAuth 2.0)
Use authorization code grant authentication for delegated user access. The connection inherits the OneLake permissions of the Microsoft user who authorizes it.
Minimum and default scopes
The connector requests the https://storage.azure.com/user_impersonation scope automatically. You don't need to assign API permissions in the Azure portal or request additional scopes.
Microsoft OneLake setup for authorization code grant authentication
Complete the following steps to set up Microsoft OneLake for authorization code grant authentication:
- Register the Workato app in the Azure portal
- Generate a client secret
- Obtain the Application (client) ID and Directory (tenant) ID from the Azure portal
Register the Workato app in the Azure portal
View register the Workato app in the Azure portal steps
Complete the following steps to register the Workato app in the Azure portal:
Sign in to the Azure portal.
Select App registrations > + New registration.
Enter a unique name for the application.
Use the Supported account types drop-down menu to select an account type.
Select Web from the Select a platform drop-down menu.
Use the following URI for the Redirect URI:
https://www.workato.com/oauth/callbackSelect Register.
Generate a client secret
View generate a client secret steps
Complete the following steps to generate a client secret:
Go to Manage > Certificates & Secrets > Client secrets.
Click + New client secret.
Provide a Description for the client secret and specify an Expires date.
Click Add.
Copy and save the client secret Value—not the Secret ID—for use in Workato.
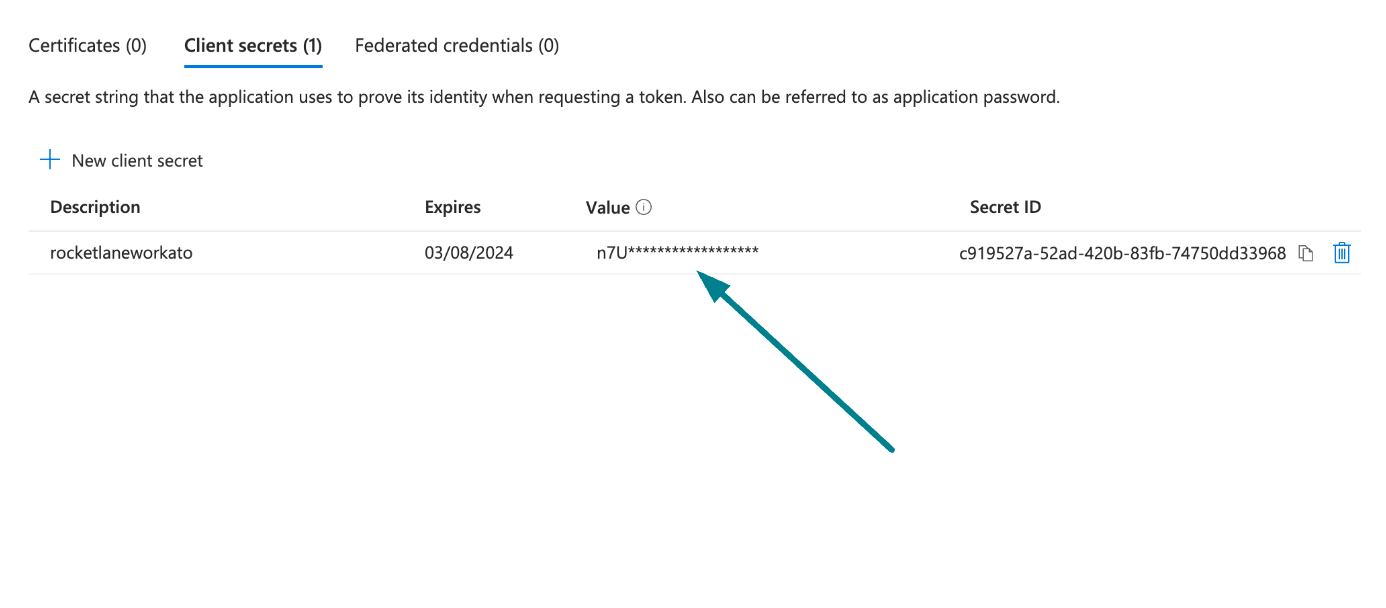 Copy and save the client secret value
Obtain the Application (client) ID and Directory (tenant) ID from the Azure portal
View obtain the Application (client) ID and Directory (tenant) ID steps
Complete the following steps to obtain the Application (client) ID and Directory (tenant) ID from the Azure portal:
Go to the Overview > Essentials section.
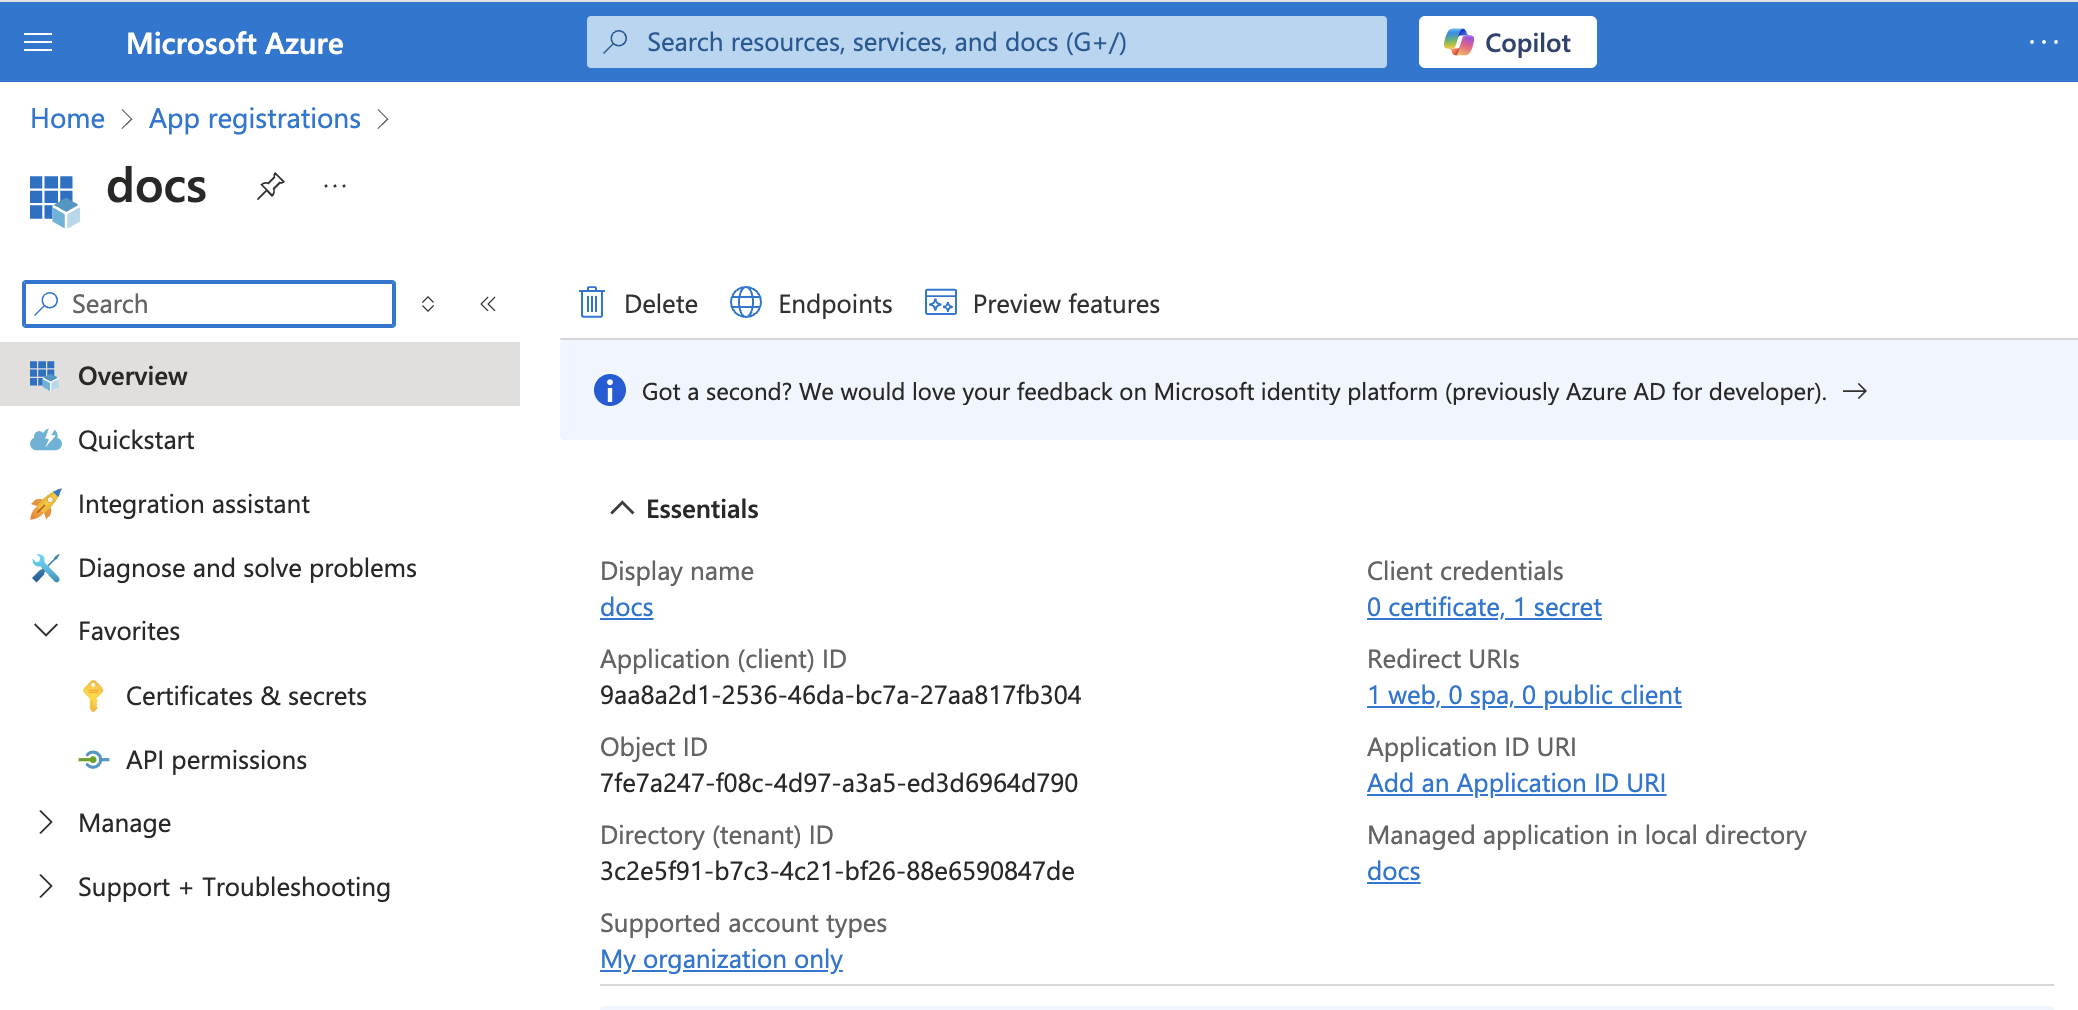 App details
Copy and save the Application (client) ID and Directory (tenant) ID for use in Workato.
Connect to Microsoft OneLake with authorization code grant authentication
View connect to Microsoft OneLake with authorization code grant authentication steps
Complete the following steps to set up an authorization code grant connection to Microsoft OneLake in Workato:
Click Create > Connection or press C twice.
Search for Microsoft OneLake and select it as your app.
Provide a name for your connection in the Connection name field.
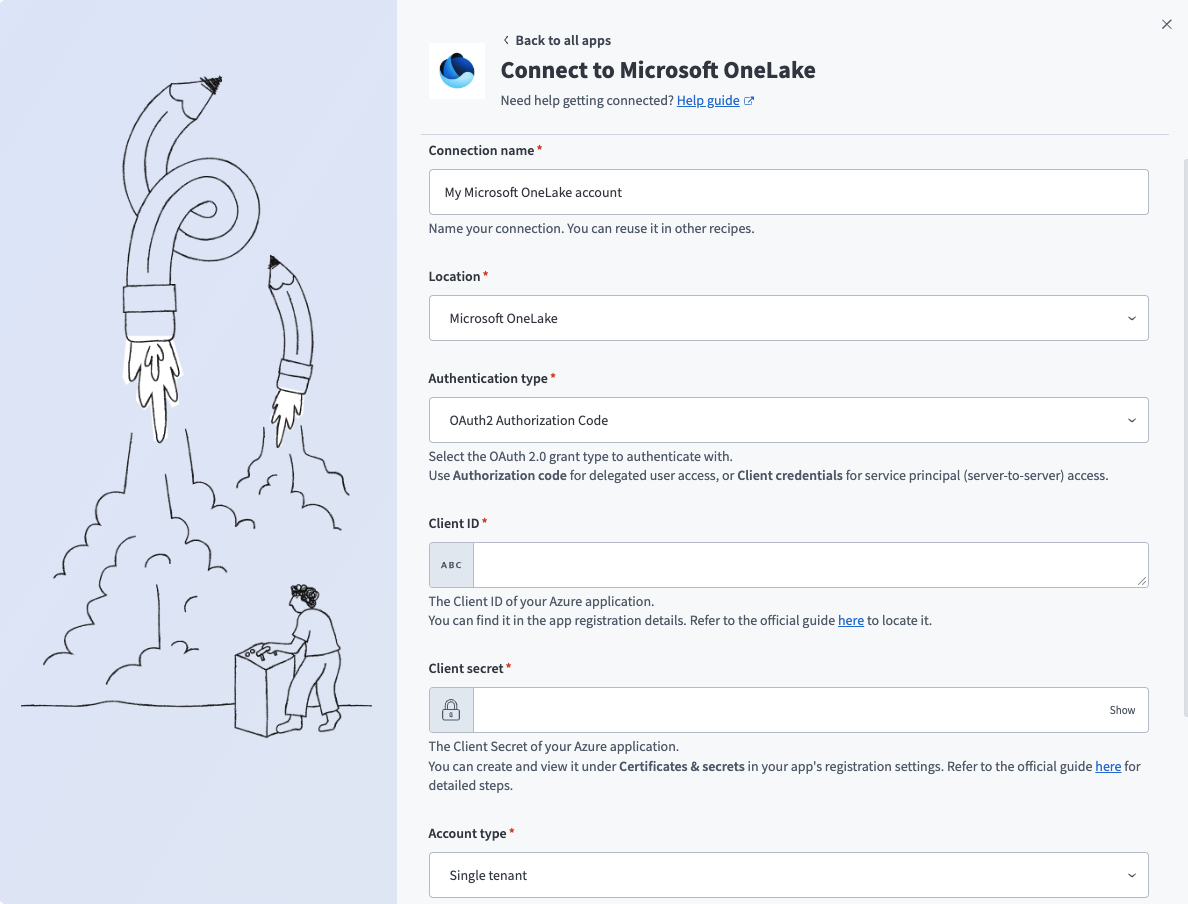 Microsoft OneLake authorization code connection
Use the Location drop-down menu to select the project where you plan to store the connection.
Use the Authentication type drop-down menu to select OAuth2 Authorization Code.
Enter the Client ID of your Azure application.
Enter the Client secret of your Azure application.
Use the Account type drop-down menu to select your Azure application's account type. Options are Single tenant, Multitenant, or Active directory multitenant. Defaults to Single tenant.
Enter the Tenant ID of your Azure application. The Tenant ID field is only available when Account type is Single tenant.
Click Connect.
Sign in to Microsoft when prompted to authorize the connection.
Client credentials-based authentication (OAuth 2.0)
Use client credentials-based authentication for service principal access that connects using the app identity instead of a signed-in user. This authentication type suits server-to-server automation that runs without a user present.
This authentication type requires the following values:
- Client ID
- Client secret
- Tenant ID
ENABLE SERVICE PRINCIPAL ACCESS
A Fabric administrator must enable Service principals can use Fabric APIs in Admin portal > Tenant settings > Developer settings. Microsoft enables this setting by default for new tenants. Refer to the Microsoft Developer admin settings documentation for more information.
Microsoft OneLake setup for client credentials-based authentication (OAuth 2.0)
Complete the following steps to set up Microsoft OneLake for client credentials-based authentication:
- Register the Workato app in the Azure portal
- Generate a client secret
- Obtain the Application (client) ID and Directory (tenant) ID from the Azure portal
- Grant the service principal access to your workspaces
Register the Workato app in the Azure portal
View register the Workato app in the Azure portal steps
Complete the following steps to register the Workato app in the Azure portal:
Sign in to the Azure portal.
Select App registrations > + New registration.
Enter a unique name for the application.
Use the Supported account types drop-down menu to select an account type.
Select Web from the Select a platform drop-down menu.
Use the following URI for the Redirect URI:
https://www.workato.com/oauth/callbackSelect Register.
Generate a client secret
View generate a client secret steps
Complete the following steps to generate a client secret:
Go to Manage > Certificates & Secrets > Client secrets.
Click + New client secret.
Provide a Description for the client secret and specify an Expires date.
Click Add.
Copy and save the client secret Value—not the Secret ID—for use in Workato.
Copy and save the client secret value
Obtain the Application (client) ID and Directory (tenant) ID from the Azure portal
View obtain the Application (client) ID and Directory (tenant) ID steps
Complete the following steps to obtain the Application (client) ID and Directory (tenant) ID from the Azure portal:
Go to the Overview > Essentials section.
App details
Copy and save the Application (client) ID and Directory (tenant) ID for use in Workato.
Grant the service principal access to your workspaces
View grant the service principal access to your workspaces steps
A service principal can only access the OneLake items you give it access to. Add the service principal to each Fabric workspace your recipes use and assign a workspace role that covers the operations you need.
DON'T ASSIGN API PERMISSIONS
Don't add Azure Storage permissions to the app registration. OneLake authorizes a service principal through Fabric workspace roles and OneLake security instead. Refer to the Microsoft Data security in OneLake documentation for more information.
Connect to Microsoft OneLake with client credentials-based authentication
View connect to Microsoft OneLake with client credentials-based authentication steps
Complete the following steps to set up a client credentials-based connection to Microsoft OneLake in Workato:
Click Create > Connection or press C twice.
Search for Microsoft OneLake and select it as your app.
Provide a name for your connection in the Connection name field.
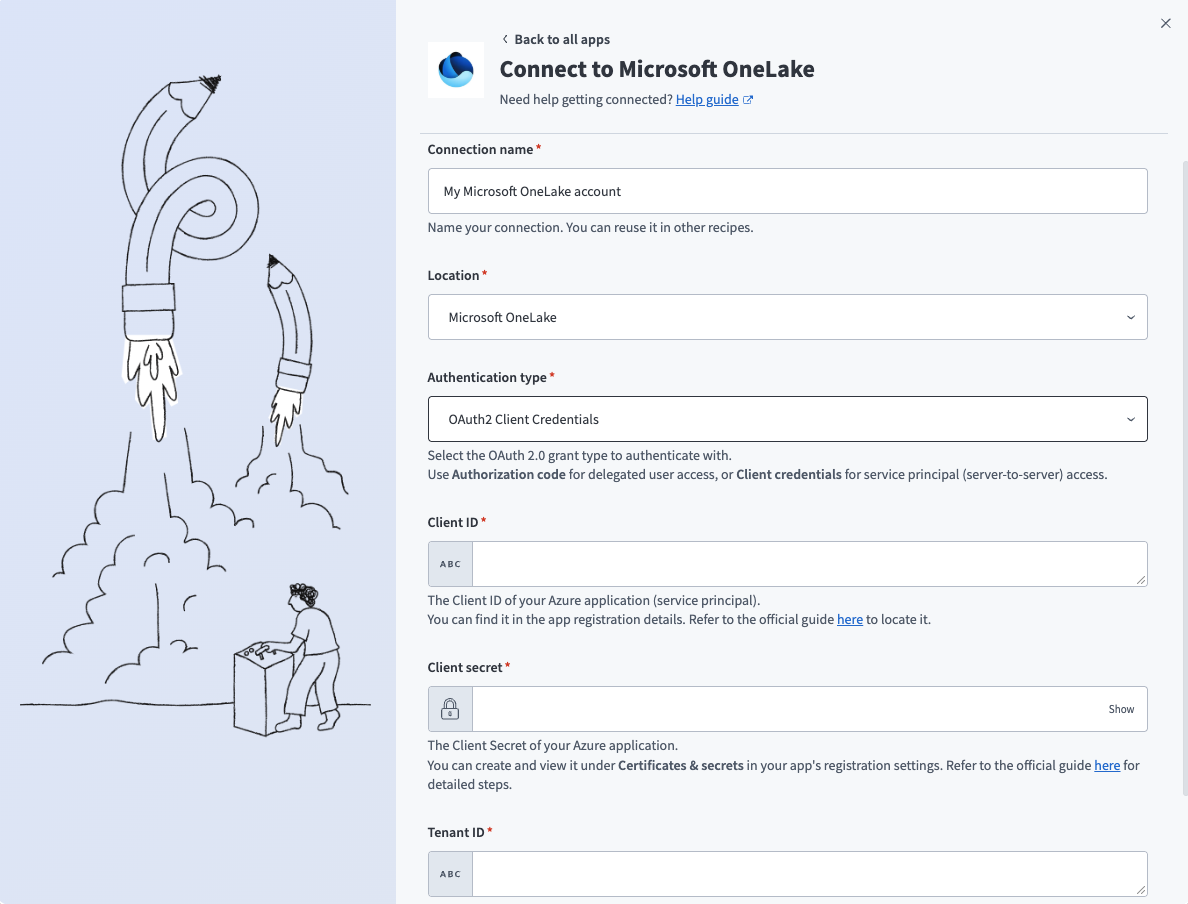 Microsoft OneLake client credentials connection
Use the Location drop-down menu to select the project where you plan to store the connection.
Use the Authentication type drop-down menu to select OAuth2 Client Credentials.
Enter the Client ID of your Azure application's service principal.
Enter the Client secret of your Azure application.
Enter the Tenant ID of your Azure application in GUID or friendly name format.
Click Connect.
Connect Microsoft Entra ID to the Microsoft OneLake connector
The Microsoft OneLake connector requests the https://storage.azure.com/user_impersonation delegated scope, which users can consent to themselves in most tenants. Complete this section only if your tenant restricts user consent and requires an admin to approve consent requests.
View connect Microsoft Entra ID to the Microsoft OneLake connector steps
To connect to the Microsoft OneLake connector using a Microsoft Entra ID account, ensure that all the consent requests are granted by admins.
Complete the following steps to grant admin consent using an admin account:
Sign in to your Azure portal and navigate to Enterprise Applications > Activity > Admin consent requests.
Approve the necessary consent requests.
Last updated: